The 30 checks below are a practical starting point for your own site or an authorized test environment. Adapt them to the features you actually have. A brochure site does not need checkout tests, and a successful homepage load does not prove that login, search or a purchase journey works.
Guides Karan Singh BhakuniUpdated 3 Nov 2026
How to Find Bugs in a Website: 30 Practical Checks
Karan Singh BhakuniUpdated 3 Nov 2026- 12 min read
- 11 sections
- 2 comparison tables
- 7 questions answered
The short answer
To find bugs in a website, choose an important user task, write down its expected result, run it in a recorded browser and device, and capture what actually happens. Use the browser’s Console and Network panels to investigate failures, then repeat the same task after a fix. Automated checks help with repeatable patterns; they cannot establish that every business rule or user experience is correct.
Want the site rather than the reading? Build one free with Grigora
Contents11 sections
Read nextHow to Legally Protect Your Blog: Practical Checks
Prepare a small, repeatable test plan
List the important templates and journeys: landing page, article, search, contact form, account and checkout where relevant. Include a recently changed page and a representative older one. Start with the tasks whose failure would prevent people using the site, lose work, send incorrect information or expose data.
| Record before testing | Example or purpose |
|---|---|
| Environment | URL, staging or production, build or release identifier and date checked. |
| Browser and device | Browser version, operating system, viewport size and whether the test used a physical device or emulation. |
| State and inputs | Signed in or out, test account role, relevant consent/settings, locale and synthetic input data. |
| Expected result | A clear outcome such as one saved request and one confirmation, not merely “the button works.” |
| Observed result | Pass, a reproducible failure, blocked or not tested, with evidence and any limitations. |
Use test accounts, synthetic data and controlled inboxes for actions that create records or send messages. Use the payment provider’s sandbox for checkout scenarios. For example, Stripe’s testing documentation describes simulated transactions that do not move funds. Keep load tests and intrusive security work in a separately agreed environment and scope.
Checks 1–5: navigation and page responses
- 1. Main navigation: Follow the primary links from a fresh page. Confirm the destination and selected state, including the phone menu. A link that opens successfully but leads to the wrong page is still a defect.
- 2. Internal article links: Open contextual links, related posts and table-of-contents anchors. Check that the target exists and a sticky header does not hide the destination heading. A crawler can collect candidates; inspect important results.
- 3. Moved pages and redirects: Visit a known old URL after a migration. Confirm it reaches the intended replacement without a loop or unrelated destination, and inspect the response chain when needed.
- 4. Missing-page behavior: Visit a deliberately nonexistent path on your test site. Check the helpful error page and HTTP status. A genuine missing resource can correctly return 404; the bug may be a broken incoming link or an incorrect 200 response.
- 5. Back, forward and refresh: Navigate through a real task, then use browser history and reload. Check filters, selected items and state as the product specifies, especially after a form or client-side navigation.
MDN’s 404 reference explains that the status means the resource cannot be found. Do not “fix” every404 by redirecting it to the homepage. Investigate whether the URL was mistyped, moved, deliberately removed or incorrectly linked.
Checks 6–10: forms, accounts and transactions
- 6. Valid form submission: Use a controlled test identity and complete the normal path. Confirm the visible success state and the expected downstream record or test email; a success message alone is not proof that the request arrived.
- 7. Invalid and boundary input: Try empty required fields, whitespace-only names, an invalid email and a reasonable long value. Check clear errors, preserved valid input and correct focus, without inventing abusive payloads.
- 8. Repeat actions and failures: In a test environment, try a double activation and a failed request. Check that the interface does not silently create duplicate records, remain stuck forever or falsely report success.
- 9. Account state and roles: With authorized test accounts, check sign-in, sign-out, recovery and the specified role differences. A hidden menu item is not proof of server-side access control; report suspected authorization problems for qualified investigation.
- 10. Checkout and receipts: In the provider’s sandbox, check successful and declined payments, cancellation, totals, currency and one matching order/receipt. Verify the full state change rather than only the payment button.
Checks 11–15: mobile, layout and media
- 11. Narrow and wide layouts: Inspect representative phone, tablet and desktop widths and nearby breakpoint sizes. Look for clipped text, overlapping controls and page-wide horizontal scrolling; a table may intentionally scroll inside its own container.
- 12. Real content: Use long titles and names, empty states and available translated content. Layouts that work only with short sample text are not ready for actual data.
- 13. Menus and overlays: Open and close navigation, dialogs, consent controls and pop-ups. Check that controls stay reachable, background overlays clear, and the page can scroll again after dismissal.
- 14. Images and downloads: Scroll through the page to trigger lazy loading. Confirm the right images, useful crops, legible diagram labels and working downloads. Check important linked files as well as the thumbnails.
- 15. Audio and video: Start, pause and seek the media. Check controls and accurate captions or other appropriate alternatives, and whether a blocked embed or slow connection produces a useful state.
Chrome’s Device Mode documentation explicitly calls emulation an approximation. It is useful for exploring widths and network conditions, but does not run the page on a mobile CPU or replace checking real touch, keyboard and browser behavior. The mobile layout troubleshooting guide explains how to narrow a specific layout difference.
Checks 16–20: basic accessibility and interaction
- 16. Keyboard navigation: Put the mouse aside. Use Tab and Shift+Tab to reach controls, then the expected activation keys. Look for a visible focus indicator and a sensible order; check that users can leave menus and dialogs.
- 17. Form labels and errors: Check that each field has an understandable label, required inputs are identified, and errors explain what to correct. An error conveyed only by a red border can be missed.
- 18. Zoom and text: Increase browser zoom and test larger text. Check that content remains available and controls usable, including fixed headers, menus and form messages. Record the actual setting used.
- 19. Meaning beyond color: Inspect important status messages, graphs and controls. Use an appropriate contrast check and make sure a color change is not the only way to understand success, failure or selection.
- 20. Structure and alternatives: Check a meaningful page title, logical headings, descriptive link/control names and image alternatives appropriate to their purpose. For a diagram, provide its useful information in accessible text too.
These are initial checks, not a declaration of conformance. W3C WAI’s Easy Checks warns that a page can pass a quick review and still contain significant barriers. Combine automated findings with manual assessment, assistive-technology testing and user involvement appropriate to your product.
Also worth readingHow to Make a Weather Website: API Example and Launch Checks
Checks 21–25: content, search and data
- 21. Search results: Try a known title, a partial phrase and a query with no match. Check relevant results, a clear empty state and filters that do what their labels say.
- 22. Dates, times and numbers: Check the displayed timezone and locale, date boundaries and any booking or price calculation using known expected values. Do not assume the tester and customer share the same timezone.
- 23. Uploads and downloads: Use benign test files within and just outside the specified size/type limits. Check validation, completion and retrieval. This functional check does not establish that the upload pipeline is secure.
- 24. Content and metadata: Verify important facts, prices, contact details, links and page-specific titles/descriptions. Confirm that intended public pages have the correct canonical and indexing settings, particularly after template or migration changes.
- 25. State persistence: Save an allowed preference or draft in a test account, navigate away and return. Check the specified behavior after refresh and in the intended account; verify that another test user does not see the wrong person’s information.
Checks 26–30: diagnostics, performance and retesting
- 26. Console evidence: Open the browser Console before reproducing the task. Note relevant errors and their timing. A warning or third-party error is a clue to investigate, not automatic proof of the root cause.
- 27. Network evidence: With the Network panel open, reload or repeat the failing action. Inspect failed requests, status, response, timing and initiator. A 200 response can still contain incorrect data; an intentionally blocked request may be expected.
- 28. Performance conditions: Test representative pages under recorded conditions. Use page diagnostics and available real-user data to investigate slow rendering or interactions, keeping controlled lab results separate from visitors’ actual experience.
- 29. Supported browsers and devices: Repeat critical journeys in the combinations your product supports and visitors use. Record the exact combinations checked. Passing one desktop browser does not establish Safari, Firefox or physical-phone coverage.
- 30. Fix verification: Re-run the original failing steps after the change, then check nearby flows that use the same component. Record the new build and result; distinguish a verified fix from an issue that simply stopped reproducing once.
Use browser diagnostics to explain a symptom
The Chrome Console exposes logged messages and JavaScript errors. The Network panel shows request activity and response details. Open the relevant panel before reproducing the issue so the evidence covers the failing action. Record only information needed for the report and remove credentials, tokens and personal data before sharing logs.
For example, if Send appears to do nothing, first check whether input validation prevented submission, a script failed before a request, the request returned an error, or the server accepted it but the success state did not appear. These are different failures with different fixes. Do not rewrite a component just because an unrelated console message is red.
For performance, PageSpeed Insights separates lab diagnostics from field data, which may be unavailable or represent the origin rather than a single page. A high score does not prove a checkout works, and one low run is not a complete diagnosis. Record the page, device/network conditions and comparable before/after measurements.
Write a bug report another person can reproduce
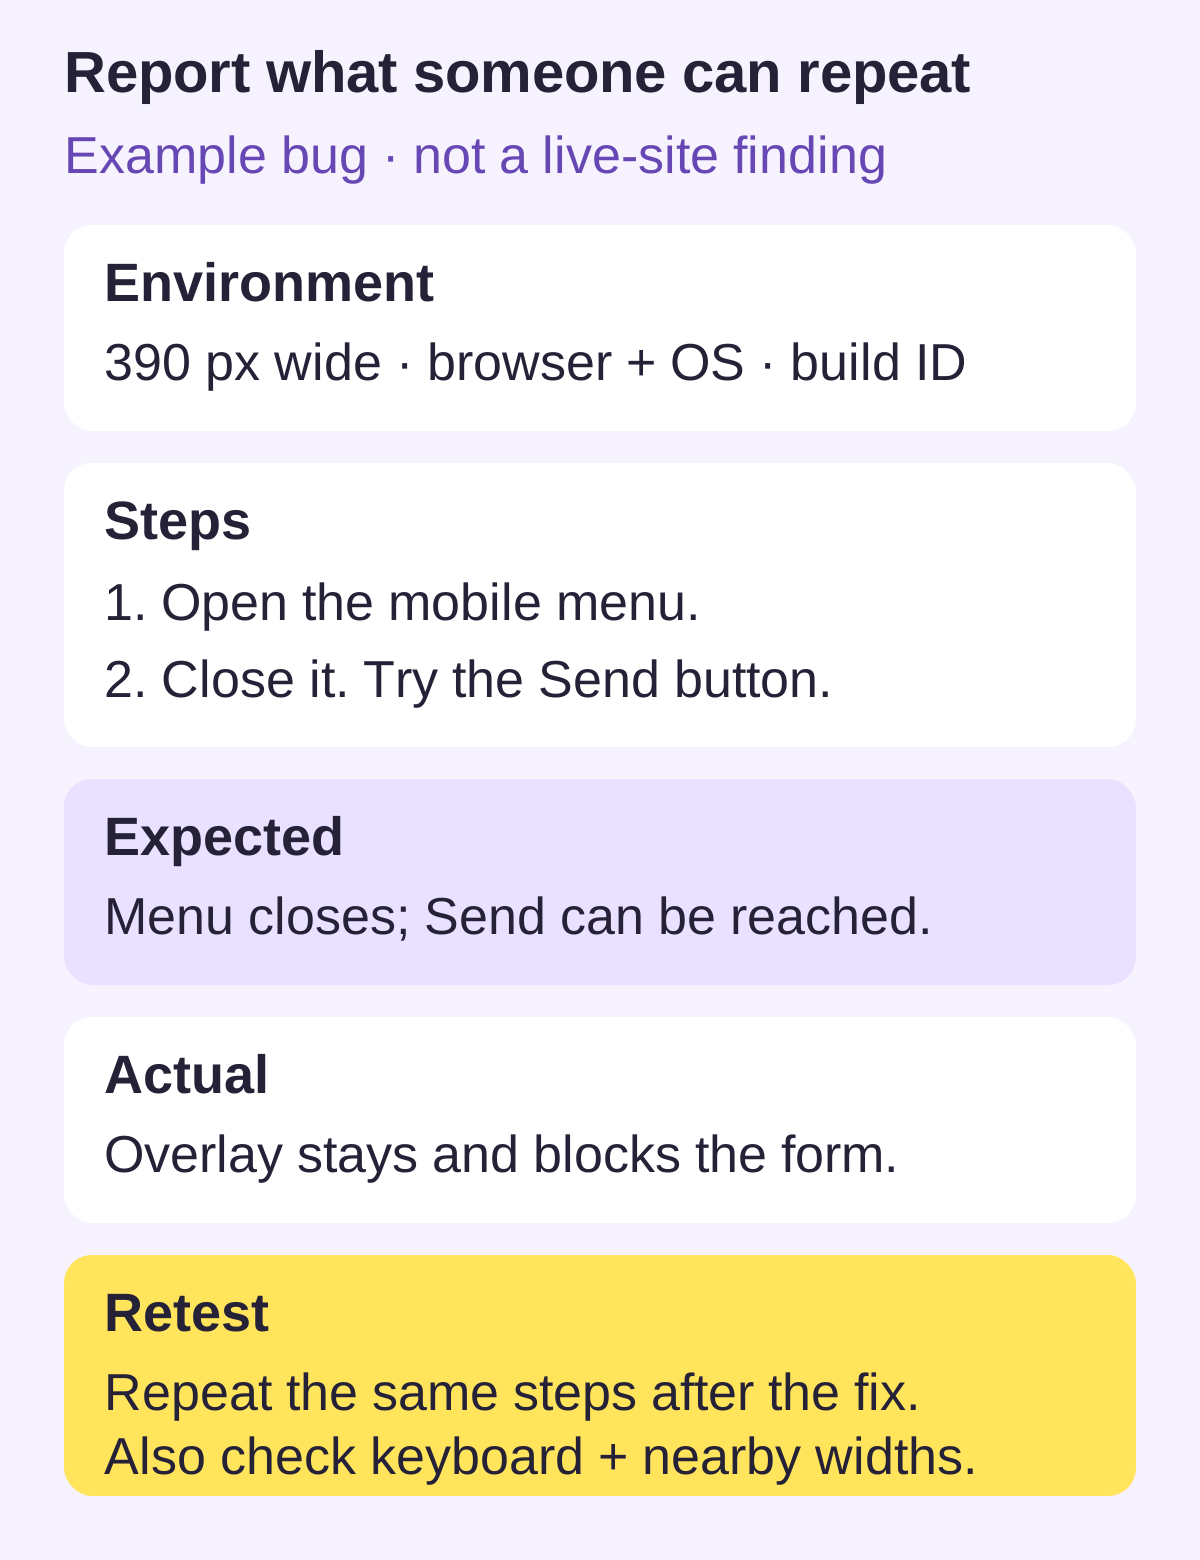
A precise report reduces the time spent guessing. Give each issue one clear title and include the environment, relevant state, numbered steps, expected result, actual result, frequency and evidence. Link related symptoms instead of combining several unrelated failures into one ticket. A spreadsheet can work; a dedicated tracker is optional.
| Example report field | Illustrative content |
|---|---|
| Title | Mobile menu overlay remains after dismissal and blocks the contact form. |
| Environment | Staging URL, release identifier, Chrome version and OS,390px viewport, signed out. |
| Steps | Open the contact page; open the mobile menu; dismiss it; try to reach Send. |
| Expected | The menu and overlay close; the form can be reached and operated. |
| Actual | The overlay stays over the page and prevents interaction. Reproduced three times in the recorded environment. |
| Evidence and impact | Screenshot or short recording; relevant diagnostics; contact journey blocked. No real customer data. |
| Retest | Repeat the exact steps after the fix, then check keyboard dismissal, adjacent widths and the shared menu on another template. |
Prioritize, fix and automate the right things
Assess user impact separately from scheduling priority. An exposed private record or a broken core transaction may need immediate containment; a cosmetic alignment issue may wait. Record affected users, scope, workaround, confidence and dependencies. Give each issue an owner and a next action rather than labeling every red tool finding critical.
Security work needs more than this checklist. The OWASP Web Security Testing Guide is a resource for developers and security professionals. Use a qualified review with agreed authorization and scope for authentication, authorization, sensitive data and other security concerns. HTTPS or a successful role-menu check alone cannot establish application security.
Automate stable, valuable regression checks after you know their expected results: a critical form, a known redirect, a calculation or a previously broken flow. Keep exploratory review for new behavior and human judgment for content, accessibility and meaningful visual changes. Avoid tests that merely confirm an element exists when the user needs a task completed.
Before publishing a fix, test in the relevant environment, review the change and keep a rollback path appropriate to the release. After deployment, verify the affected public behavior and monitor for related failures. Keep a coverage record: passed, failed, blocked and not tested. No finite test pass proves a website is completely bug-free.
Website bug finding FAQs
Follow important tasks with known expected outcomes, check links and forms using controlled test data, try keyboard navigation and inspect representative phone and desktop layouts. Record exact steps and evidence. A developer or specialist can investigate technical, security or accessibility findings that need deeper assessment.
No. A scanner can detect patterns within its scope, but may miss business-rule errors, account states, meaningful content mistakes and barriers requiring human judgment. Use tool findings as evidence to investigate and record what the scan actually covered.
No. A missing resource can correctly return 404. Investigate whether a link points to the wrong place, a moved page needs an appropriate redirect or a custom missing-page screen returns an incorrect success status. Do not send every missing URL to an unrelated homepage.
It is useful layout and condition simulation, but it is not physical-device testing. Record it as emulation. Test important journeys on real supported devices and browsers when that coverage is needed.
Test changed features and important shared components before release, verify the deployed behavior, and repeat critical journeys as the site and its dependencies change. The appropriate ongoing schedule depends on the product, risk and release pattern; there is no universal interval.
Include a clear title, URL and build, browser/device/state, exact steps, expected and observed behavior, frequency, impact and relevant evidence. Remove sensitive data from screenshots and logs. State what will count as a verified fix.
Record the conditions and frequency instead of marking it fixed after one successful attempt. Note time, account state, network conditions and relevant logs, then try to isolate one variable at a time. If evidence is insufficient, mark the issue intermittent or blocked and define the next investigation.
Practical writing on building a site, growing an audience and sending email people open. No more than one a week.

Karan Singh Bhakuni
118 articles on the Grigora blog
More on Guides
Guides
How to Legally Protect Your Blog: Practical Checks
Reduce avoidable blogging risks by checking what you publish, own, collect and sell. Learn which documents and operating practices need review.
31 Oct 202310 min read
Guides
How to Make a Weather Website: API Example and Launch Checks
Start with one location and a suitable data source. Use a small prototype, then check timestamps, units, error states, privacy and provider terms before adding features.
10 Oct 202310 min read
Guides
How to Write Blog Posts Faster: 30 Practical Tips
A practical workflow and 30 writing tips, with a reusable brief and a timing worksheet to improve your process while keeping accuracy and review in place.
16 Nov 202312 min read